


What is LeakRadar?
LeakRadar by Radrly is a Jira and Confluence Cloud app (Atlassian Forge) that finds leaked secrets (API keys, passwords, tokens) and personal data inside Atlassian, helps triage them with AI that runs inside Atlassian, and keeps signed evidence.
Free trial on Atlassian Marketplace. One Jira licence covers Confluence too. Runs on Atlassian, zero egress.
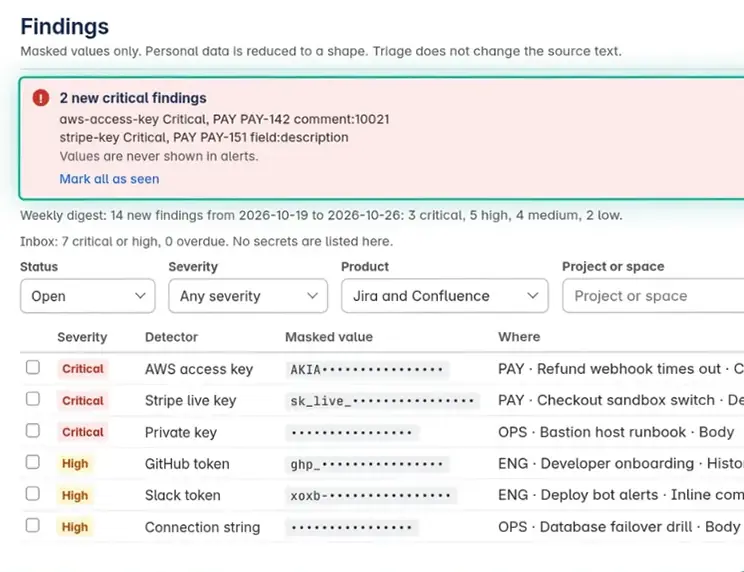
- 2 new critical findings
- 14 new findings in the weekly digest
Who it is for
LeakRadar by Radrly is for security, privacy and platform teams on Jira Cloud and Confluence Cloud. A Jira administrator installs and configures it. The LeakRadar team and people with delegated roles work on findings in their own projects and spaces. One licence covers both products on the same site.
The problem it solves
API keys, passwords, tokens and personal data often end up in Jira work items and Confluence pages, including comments, history, versions, attachments and text in images. LeakRadar finds those secrets and that personal data, helps you triage them and clean them up, and keeps a masked record of what was found and where. See the guides on finding leaked credentials and on DLP for Jira and Confluence.
How it works
- Install it from Atlassian Marketplace on a Jira Cloud site, then connect Confluence Cloud on the same site if you want pages scanned too.
- Choose the scan scope and start the first scan. A backfill covers recent history, then product events keep scans live.
- Detectors find secrets and personal data. Built-in detectors cover API keys, tokens, passwords, private keys and connection strings, including Hugging Face, Linear, Sentry, Slack app-level tokens, Fly.io, PlanetScale, Doppler and Terraform Cloud, plus card numbers, IBAN and SWIFT codes, national IDs from 13 countries, health identifiers and passport MRZ lines. Forge LLMs review only ambiguous matches, and they see detected values only as placeholders.
- Triage, then clean up. Assign owners, rotate or revoke a secret first, then redact, purge older Confluence versions and handle attachments. The Erasure screen helps you find personal data for a data subject request; it is not legal advice.
- Standard covers scanning, triage, remediation, policies and DSAR. Advanced adds the Rovo agent, the Rovo MCP server, signed evidence packs and real-time critical alerts. Prices for your user tier are on the Atlassian Marketplace pricing tab.
What is different about it
- Runs on Atlassian, with zero egress. Built on Forge: no external hosts, no Forge Remote and no web triggers. See Security.
- AI inside Atlassian. Forge LLMs never see the real secret or personal data value, only a placeholder.
- Masked, hashed, located. Only a masked snippet, a per-install HMAC fingerprint and the location are stored.
- Rotate first. LeakRadar cannot check whether a secret is still active at its provider, because that would need a call outside Atlassian.
Where to install it
Install LeakRadar from its Atlassian Marketplace listing. A Jira administrator installs it on a Jira Cloud site, then connects Confluence Cloud on the same site in Atlassian Administration, with the same licence. Setup steps are in the documentation, and the product tour video walks through the app.
Who makes it
LeakRadar is made and supported by Radrly (Radrly Sp. z o.o.), which builds Atlassian Forge apps for Jira and Confluence Cloud, including MarginRadar, AccessRadar, ConfigRadar, LimitRadar and CapRadar. Support is at support@radrly.com.
Frequently asked questions
What is LeakRadar for Jira and Confluence?
LeakRadar by Radrly is a Jira and Confluence Cloud app (Atlassian Forge) that finds leaked secrets (API keys, passwords, tokens) and personal data inside Atlassian, helps triage them with AI that runs inside Atlassian, and keeps signed evidence. One licence covers Jira Cloud and Confluence Cloud on the same site. Signed evidence packs, the Rovo agent and the Rovo MCP server are part of the Advanced edition.
Is LeakRadar by Radrly related to leakradar.io?
LeakRadar by Radrly is an Atlassian app for Jira and Confluence. It is not affiliated with leakradar.io, a separate breach search service.
Does data leave Atlassian?
No. LeakRadar itself has zero egress: no external hosts, no Forge Remote and no web triggers. AI triage uses Forge LLMs inside Atlassian, and every detected value is replaced by a placeholder before the model sees the text. Findings live in Forge hosted storage. LeakRadar never stores a full secret or personal data value, only a masked snippet, a per-install HMAC fingerprint and the location. Optional MCP access is off by default and is controlled by a site or organisation admin.